A vulnerability report reduces risk only when findings lead to verified changes. Build a workflow for ownership, prioritisation, exceptions and retesting.
Create a trustworthy findings register
Combine assessment results with the asset inventory, business owner and service criticality. Preserve the source, observation date and evidence for each finding. Deduplicate repeated detections without losing affected instances. Mark uncertain results for validation and record assets that could not be tested. A shrinking spreadsheet is not meaningful if coverage is shrinking too.
Prioritise exposure and business impact
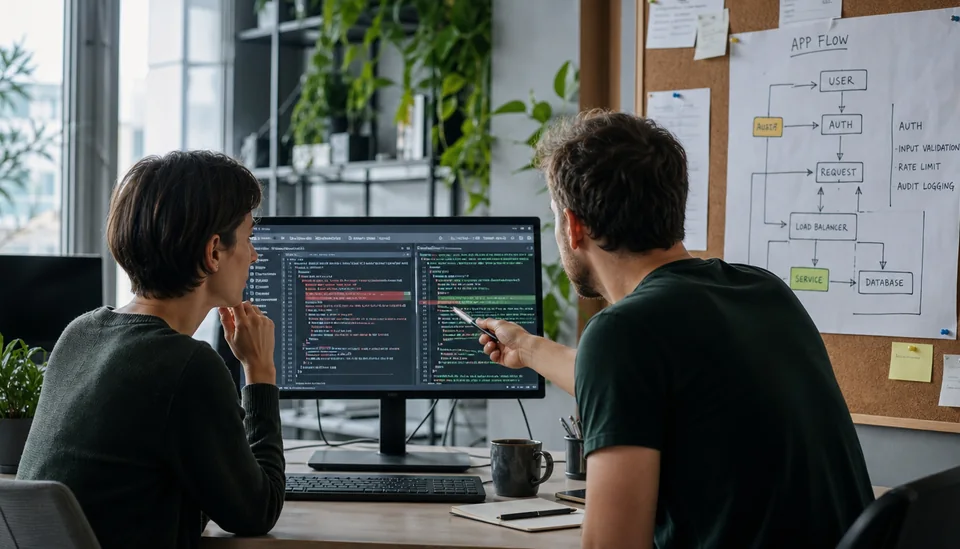
Consider internet reachability, exploit prerequisites, available privileges and the value of the affected service. A moderate issue on a payment approval path can matter more than a higher-scoring issue in an isolated test environment. Record the reason for priority decisions and review it when exposure changes. Temporary compensating controls need an owner and an expiry date.
Make remediation operationally safe
Agree a fix, maintenance window, rollback procedure and acceptance test with the system owner. Track dependencies such as unsupported software or vendor access. When a fix is delayed, document the residual risk and the authorised decision rather than silently closing the ticket. Keep sensitive evidence accessible only to people who need it.
Retest and report outcomes
Verify that the original weakness is addressed and that the change has not created a new access path. Distinguish fixed, partially fixed, accepted and unverified findings. Report ageing, recurrent issues and validated closure, with coverage limitations visible. TRUST-IT supports assessment and retesting so technical teams and management can review evidence of risk reduction.