A useful cybersecurity assessment connects technical findings to business decisions. Define the questions, evidence and remediation process before testing begins.
Start with the business question
List the services you cannot afford to lose and the data or approvals an attacker would value. An assessment of an internet-facing application answers different questions from an internal identity review. Identify system owners, third-party dependencies and the decisions the final report must support. Agree exclusions explicitly so an untested system is never mistaken for a secure one.
Select complementary assessment methods
A vulnerability assessment can identify known exposures across a defined asset inventory. Penetration testing examines whether selected weaknesses can be used within authorised rules of engagement. Source code review can uncover logic and trust-boundary issues that external scanning cannot establish. Choose the methods needed for the risk question; buying all three without a coherent scope can still leave important gaps.
Require evidence and safe execution
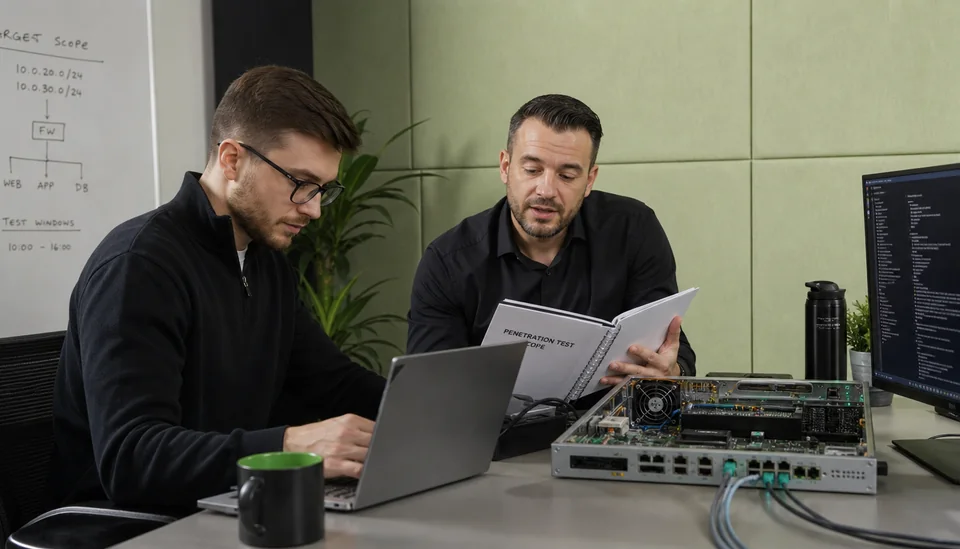
Specify testing windows, test accounts, prohibited actions, escalation contacts and a stop procedure. Findings should identify affected assets, prerequisites, reproducible evidence and a realistic impact explanation. Sensitive evidence belongs in controlled delivery channels. Reports should distinguish confirmed findings from hypotheses and explain limitations caused by unavailable access or incomplete coverage.
Assign remediation and verify the result
Give each accepted finding an owner, target date and acceptance criterion. Prioritise exposed, exploitable weaknesses affecting important services before spending effort on low-impact scanner noise. Validate fixes through an agreed retest and document residual risk. TRUST-IT can help define and perform the assessment, then support a practical remediation plan with your technical team.