Connect security controls to the systems and people who operate them. TRUST-IT supports firewall and network-security integration, identity and access management, central logging and security-tool deployment within an agreed scope.
Start with an inventory, approved data flows and a target architecture. Test changes in a suitable environment, agree a maintenance window and retain a rollback path. Validate permitted and denied access, logging and escalation after deployment. Operational handover should include configurations, ownership, monitoring dependencies and maintenance instructions. Coverage hours and response commitments are agreed separately.
NETWORK INTRUSION DETECTION/PREVENTION
-
Site assessment and strategic network design guidance
-
IDS/IPS appliance installation, configuration and tuning
-
Creation of detection policies; update and tuning on an ongoing basis
-
Continuous device upgrades, patch management and device configuration maintenance
-
Network event monitoring
-
Real-time Network Intelligence
-
Real-time User Intelligence
-
Real-time Detection, Response, and Escalation of known security threats
-
Comprehensive reporting; on-demand and scheduled
-
Real-time reporting and alerting for all security events.
-
Device health and performance monitoring
-
Full backup and recovery of configurations and detection policies
-
Customer notification of major security, health, intrusion events
-
24x7x365 IDS/IPS device monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
NETWORK FIREWALL(S)
-
Site assessment and strategic network design guidance
-
Firewall policy design, device installation and configuration
-
Continuous Rule-Set validation, verification, tuning, and optimization
-
Continuous review of firewall policy and firewall security posture
-
Continuous firewall upgrades, patch management and device configuration maintenance
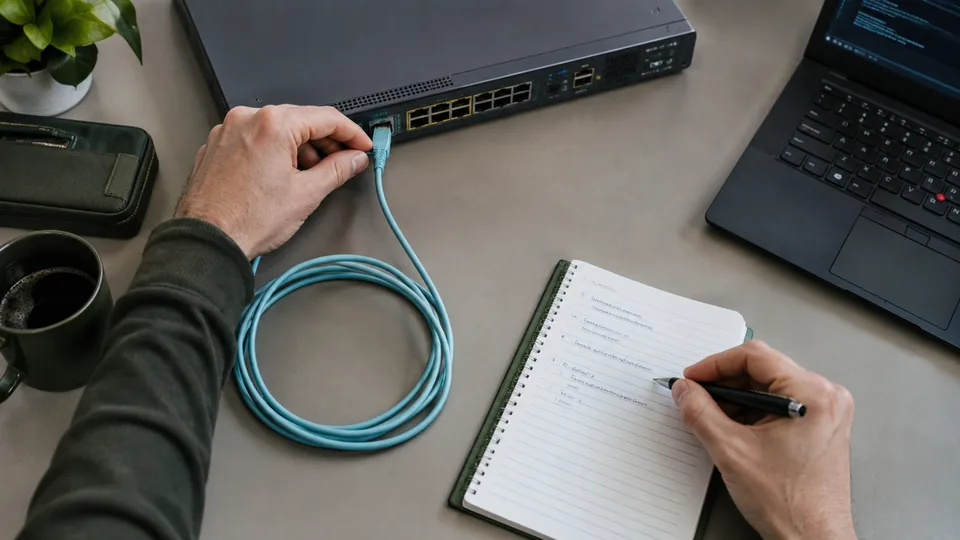
Firewall engineer updating a network appliance with a console cable and change record. -
Continuous log monitoring, analysis and archival
-
Comprehensive reporting; on-demand and scheduled
-
Device health and performance monitoring
-
Full backup and recovery of firewall configuration
-
Firewall fault analysis and problem resolution
-
24x7x365 Firewall device monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
NETWORK ADMISSION CONTROL
Site assessment and strategic network design guidance
NAC policy design, platform installation and configuration
Define and enforce corporate network security posture through NAC Platform
Continuous monitoring of secure relationships between specific network resources, users, for specific time intervals
Continuous tracking of individual users or hosts independent of their IP addresses.
Continuous protection against various network intrusions and illicit access, whether from inside or out.
Provides a clear path to enhanced compliance and auditing requirements.
-
Handles security and access for remote and mobile workers.
-
Central Management through web-based console
-
Comprehensive reporting; on-demand and scheduled Full backup and recovery of configuration
-
24x7x365 NAC Platform monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
VIRTUAL PRIVATE NETWORKS
Site assessment and strategic network VPN design guidance
VPN architecture design, equipment installation and configuration of any VPN solution
VPN Solutions include : SSL VPN Remote Access, IPSec VPN Remote Access, Site-to-Site VPN, DMVPN, GET VPN
Configuration and management of VPN Routers, Concentrators, VPN Appliances
Continuous log monitoring and log archival
Continuous VPN architecture tuning and optimization
VPN troubleshooting
-
VPN User provisioning, account creation/deletion, logging, and auditing
-
Integration with MS Active Directory and SSO, Tokens etc
-
Token life cycle management and token provisioning
-
Comprehensive reporting; on-demand and scheduled
-
Complete backup and recovery of configurations and security policies
-
24x7x365 VPN equipment monitoring and management
-
24x7x365 On-site Support in Case of Emergency
ENDPOINT SECURITY
Site assessment and strategic network design guidance
Endpoint security policy design, platform installation and configuration
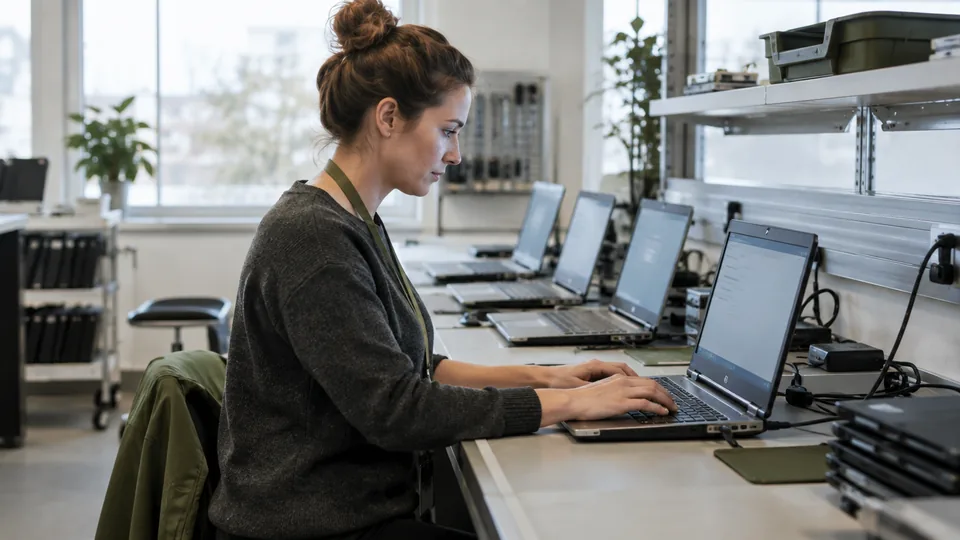
Endpoint specialist applying device security policy to a row of business laptops on a setup bench. Customized security policy design and tuning
Immediate response to prevent hacker attacks directed at your protected servers/desktops
Real time, behavior-based attack blocking
Elimination of known and unknown attacks (zero day)
Immediate updates as new attacks are identified
In-depth logging and reporting on attempted intrusions
-
Superior protection against buffer overflow, port scans and SYN floods
-
Comprehensive reporting; on-demand and scheduled
-
Real-time reporting and alerting for all security events.
-
Customer notification of major security, health, intrusion events
-
Central security policy management
-
24x7x365 device monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
DATA LEAKAGE PREVENTION (DLP)
-
Site assessment and strategic network design guidance
-
DLP policy design, platform installation and configuration
-
Define and enforce corporate network security posture through DLP Platform
-
Creation of DLP policies; update and tuning on an ongoing basis
-
Continuous monitoring of data in use (e.g endpoint actions) between specific network resources and users.
-
Continuous monitoring of data in motion (e.g network actions) between specific network resources and users
-
Continuous monitoring of data at rest (e.g data storage) between specific network resources and users.
-
Continuous device upgrades, patch management and device configuration maintenance
-
Central Management Framework
-
Real-time reporting and alerting for all security events.
-
Comprehensive reporting; on-demand and scheduled
-
Full backup and recovery of configuration
-
Customer notification of major security events
-
24x7x365 DLP Platform monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
WIRELESS NETWORK SECURITY
-
Wireless equipment installation and configuration
-
Use of the latest authentication and encryption schemes
-
Continuous visibility of who is connected through intelligent management
-
Real-time spectrum and protocol visibility
-
Wireless location tracking – to detect rogue or unauthorised access point in the network.
-
Centralized configuration management of Wireless Devices
-
Wireless IPS – to detect Wireless based intrusions.
-
Customer notification on unauthorized access
Email infrastructure engineer checking message gateway configuration beside a server cabinet. -
Comprehensive reporting; on-demand and scheduled
-
24x7x365 wireless equipment monitoring and management
-
24x7x365 monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
-
E-MAIL SECURITY
Site assessment and strategic network design guidance
E-mail Security Gateway policy design, device installation and configuration
Integration with MS Exchange Server and any Linux
E-mail Servers Protects against spam, malware, viruses, Trojans, worms, directory harvests, phishing, spyware, and malicious content in one solution
Continuous device upgrades, patch management and device configuration maintenance
Real-time reporting and alerting for all security events.
-
Comprehensive reporting; on-demand and scheduled
-
Full backup and recovery of configuration
-
Customer notification of major security events
-
24x7x365 appliance monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
APPLICATION FIREWALL
Site assessment and strategic network design guidance
Next Generation Firewall
Application Firewall security policy design, device installation and configuration
Continuous application protocol detection and decryption
Continuous application protocol decoding
Design specific application usage policies for specific groups or users through MS Active Directory
Integration Configuration and tuning of on-board Intrusion
Prevention Engine Improves network visibility by accurately identifying application traffic irrespective of port and protocol.
-
In-depth logging and reporting on attempted intrusions through applications used
-
Continuous log monitoring, analysis and archival
-
Comprehensive reporting; on-demand and scheduled Device health and performance monitoring
-
Full backup and recovery of firewall configuration
-
24x7x365 Firewall device monitoring and management
-
24x7x365 log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
WEB CONTENT SECURITY
Web Security Gateway policy design, device installation and configuration
Malware inspection of HTTP and HTTPS traffic, with detection performance assessed for the configured platform.
Multiple Anti-Virus engines used for scanning all Web traffic
Continuous scanning for P2P, IM, spyware, Trojans etc.
Continuous SSL Inspection
Continuous log monitoring, analysis and archival
Systems operator reviewing log collection and service health on a dual screen workstation.
-
Comprehensive reporting; on-demand and scheduled
-
Continuous upgrades and device configuration maintenance
-
24x7x365 device monitoring and management
-
24x7x365 monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
WEB APPLICATION FIREWALL
-
Site assessment and strategic network design guidance
-
WAF policy design, device installation and configuration
-
Continuous Rule-Set validation, verification, tuning, and optimization
-
Continuous review and tuning of WAF policy and detection rules.
-
Continuous Web Application profiling.
-
Continuous Inbound and Outbound traffic analysis
-
Continuous WAF upgrades, patch management and device configuration maintenance
-
Continuous log monitoring, analysis and archival
-
Comprehensive reporting; on-demand and scheduled
-
Device health and performance monitoring
-
Full backup and recovery of WAF configuration
-
Customer notification of major security, health, intrusion events
-
Automates web application compliance to regulations and industry standards
-
24x7x365 WAF device monitoring and management
-
24x7x365 intrusion log monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
DIRECTORY SERVICES
Trust-IT can provide a range of Directory Server solutions dedicated to any of the applicable industry verticals like Finance, Manufacturing, Insurance, Retail, Telecom etc. Directories are becoming integral part of any business in the current market scenario. The services that are mentioned below are targeted towards those customers who use or are planning to use a Directory server based mechanism which will be the central repository for any services like Authentication, Authorization, User Management, Contact No.’s & Address Management, and a gamut of other useful purposes. Trust-IT’s directory services include Consultancy, Directory Services Deployment, Directory Migration Services, Directory Security Implementation, Content Monitoring & Sustenance Service, Directory Server Sizing & Replication Strategy Planning, Application Integration.
IDENTITY AND ACCESS MANAGEMENT
Identity and Access Management (IDAM) is the comprehensive management and administration of user permissions, privileges and data which is required to bring about the true real-time enterprise. Identity management lifecycle spans creation, modification to eventual retirement of user access rights and entitlements. Trust-IT can help an organization to automate complex user management processes and to achieve:
Identity engineer reviewing central access records with a smart card reader and printed role matrix. -
Unified and centralized view of all user credentials
-
Automatic provisioning/de-provisioning of users in multiple applications, platforms and network
-
Delegated administration
-
User Self Service
-
Improved enterprise security
-
Reduced Help Desk Costs
-
Enhanced Productivity
-
Improved Regulatory
-
Compliance Directory Solutions
-
Authentication Solutions
LOG MANAGEMENT AND REPORTING
Implementing a robust yet streamlined log management solution can significantly increase any organization’s benefits from log data, both in security and compliance as well as operational efficiency. Increase your visibility into security event and network data by monitor, correlate and analyze billions of log events per day from security and network appliances, operating systems, databases, and applications.
SECURITY INCIDENT MANAGEMENT
Computer security incident management involves the monitoring and detection of security events on a computer or computer network, and the execution of proper responses to those events.
Trust-IT can help any organization to immediately detect and response to any kind of threat before it’s too late.
REAL TIME SECURITY EVENT MONITORING
Site assessment and strategic network design guidance
Appliance installation, configuration and tuning
Centralized security logs collection in real time
Integration with 3rd Party Compliance tools
Real-time Detection, Response, and Escalation of known security threats
Continuous investigation on security events
Multiple vendor security devices support; firewalls, IDS/IPS,HIPS etc
Comprehensive reporting; on-demand and scheduled
-
Real-time reporting and alerting for all security events.
-
Continuous event monitoring, analysis and archival
-
Customer notification of major security, health, intrusion events
-
Full backup and recovery of configurations
-
24x7x365 device monitoring
-
24x7x365 event monitoring, analysis, correlation, and notification
-
24x7x365 On-site Support in Case of Emergency
SECURITY VULNERABILITY SCANNER
-
Site assessment and strategic network design guidance
-
Scanner installation, configuration and tuning
-
Integration with 3rd Party Compliance tools
-
Scheduled and on-demand scanning
-
Comprehensive reporting; on-demand and scheduled
-
Customer notification for vulnerabilities and patches missing
-
Full backup and recovery of configurations
-
24x7x365 device monitoring
-
24x7x365 monitoring, analysis, correlation, and event notification
-
24x7x365 On-site Support in Case of Emergency
-
Plan integration around real data and access flows
Before connecting systems, identify which information must move, which identities need access and which business process depends on the connection. The design should define normal operation and what happens when a provider, interface or source record is unavailable. These decisions apply to network, application and AI-assisted integrations alike.
A controlled implementation includes change ownership, validation and a route back if the workflow fails. The handover should make configuration, renewal and support dependencies visible to the operating team. Existing providers can remain involved through an agreed responsibility model rather than an informal division of tasks.